

Softswiss leaders tout personalisation, AI & cyber
Fri, 25th Sep 2026 (Today)
Softswiss executives said personalisation in product design and AI in engineering are reshaping how digital platforms operate at scale. Their comments placed the company in two debates now spanning iGaming, payments and software development.
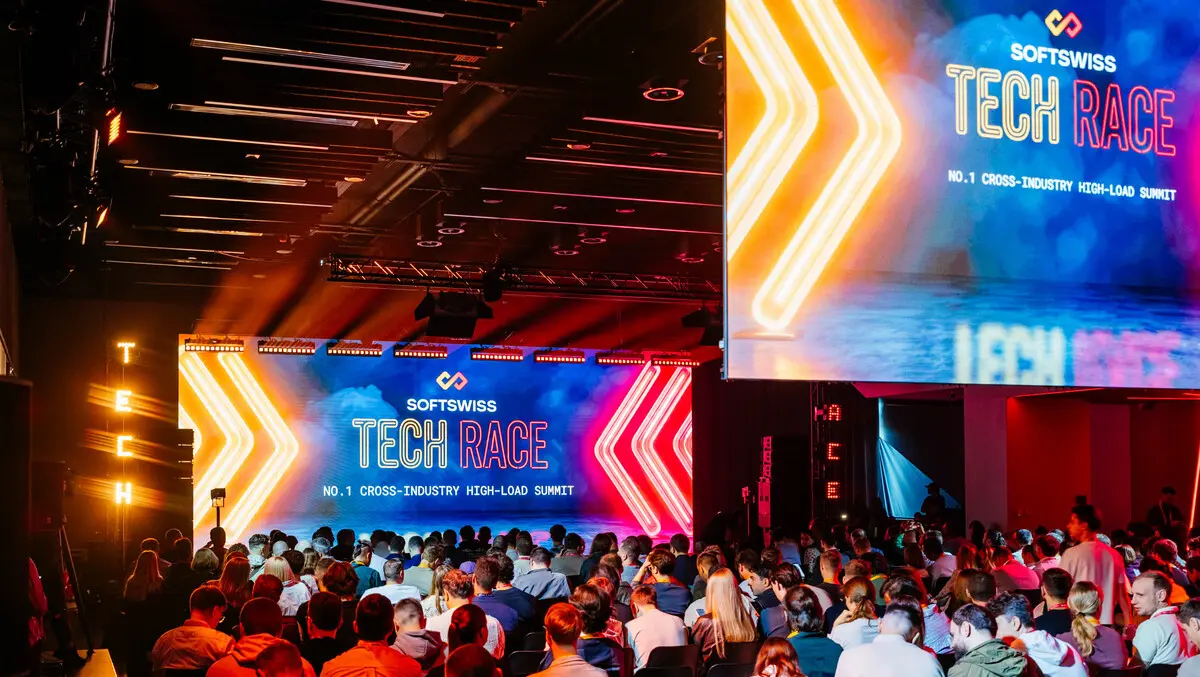
At industry panel discussions, senior Softswiss leaders outlined what they see as the next pressure points for operators, suppliers and technology teams. Their remarks covered gamification, one-to-one product journeys, AI-assisted coding, internal automation and cyber risk.
In the product discussion, Kyryl Avdienko, Chief Product Officer at Softswiss, argued that gamification has reached a point where simple imitation no longer delivers results. Many mechanics are now treated as standard features rather than points of distinction, he said.
"It's everywhere, maybe because it has already become a market standard. RPGs and MMORPGs raised a whole generation with these mechanics, and mobile gaming then brought them into mass adoption. Now we're seeing them everywhere. But the question is how people use them. All of these mechanics are designed to capture the user's attention, and blindly copying them does not always work. It can feel fragmented. What was supposed to be an engagement roadmap for retaining a client can instead become noise and distraction. For me, we have a simple test. Does the feature we created remain interesting to the player if we remove the bonus or reward? If the answer is no, then we have simply created another bonus-driven feature. The bonus is the main idea, rather than the experience itself. Only a truly meaningful experience created through gamification can bring real uplift. So the bar is quite high right now."
That view reflects a broader shift in digital consumer products. Operators may have access to the same games, payment providers and CRM tools, but execution at the product layer still separates stronger performers from weaker ones.
Avdienko also described how Softswiss first approached gamification several years ago, when the category was less established in iGaming. The aim, he said, was differentiation and product testing rather than following a fixed market formula.
"Well, it was two things. The first one is that we wanted to differentiate, we wanted to bring some extra value to the player-not to be the same content, same idea, same payment. We wanted to create something new, this extra layer that can engage the player, because at that time just adding this Wheel of Fortune already felt like a novelty and gave some value, and you didn't need to think about some complicated stuff. And the second one, for sure, was the idea that each idea needs to be validated. You need to take your bet, risk, and create something new. That's how success is made."
Personalisation shift
The discussion then moved from gamification to personalisation. Speakers from platform, payments and supplier businesses argued that the market is moving away from standard campaigns aimed at broad customer groups.
For Softswiss, the key question is whether personalisation can work across very large user bases without collapsing under its own complexity. Avdienko said the challenge is less about treating every player as a separate segment and more about building a system that can respond to behavioural patterns.
"Personalization sounds hard sometimes, but the real cost is hidden. If you're talking to 1 million users, for example, in reality it's not about 1 million segments, it's a couple thousand segments. Because for sure we are all unique individuals, but still we act in behavioral patterns. AI helps us automate this work, so users jump from one segment to another based on their actions and progress. But the real hidden cost is data and how we work with it. If we don't have enough data, we won't understand preferences. If we fail with accuracy, we can deliver a wrong message to a wrong segment. And if our data comes too late, we might try to catch somebody who already left and forgot what he was doing 15 or 30 minutes ago. That buzzword 'real-time' is where the real technical hard point lies. Right timing for the right audience with the right offer-that is the idea of personalization. And for sure, it will feel like it's tailored specially for you."
His comments point to a familiar issue for platform companies. The value of AI-led targeting depends on data quality, speed and accuracy. If any one of those weakens, the experience can become irrelevant or counterproductive.
The same tension appeared in the payments discussion. Anna Pudova, Chief Product Officer at FinteqHub, said financial journeys require reliability ahead of novelty. Payment design can still draw from gamification thinking, she argued, but only where the result is lower friction and a clearer transaction flow.
Others on the panel said one-size-fits-all mechanics are likely to fade. They expect deeper tailoring around preferred payment methods, bonus offers and content choices. The emphasis is shifting from broad personalisation towards what some panellists described as individualisation.
Engineering debate
Softswiss also took part in a wider discussion about AI in software engineering leadership. Sergey Kastukevich, Chief Technology Officer at Softswiss, moderated a panel examining whether AI has changed how technical teams are managed, how investment decisions are made and where productivity gains are likely to land.
The discussion showed little agreement on whether AI has changed engineers themselves. Some panellists said staff motivations remain broadly the same. Others said team structures built around autonomy are already better placed for the next phase of adoption.
A recurring theme was that AI should be treated as leverage rather than a substitute for judgment. Several speakers argued that management basics remain intact, even if AI tools may reduce routine administrative work.
The panel also spent considerable time on internal investment priorities. Suggestions ranged from data quality and security to company adaptability, internal automation and management education. One clear thread ran through the exchange: organisations that automate weak processes will simply multiply the problems they already have.
That point matters for large technology employers such as Softswiss because engineering efficiency is now tied more closely to organisational design. Faster code generation does not remove the need for clear ownership, quality control and resilience in production systems.
Panellists also raised a warning for senior leadership teams. Several said many executives still lack a direct understanding of AI tools, even while asking their organisations to use them more widely. The gap is no longer only a technical training issue. It affects budgeting, governance and the credibility of performance assessments.
Cyber pressure
Security formed the third strand of the discussion. Artem Bychkov, Deputy Chief Security Officer at Softswiss, took part in a panel on AI and cyber risk focused on attack surfaces, supply-chain exposure, AI agents and security operations.
Bychkov said the company's architecture limits the spread of damage from a breach, but added that even a compromise affecting a small part of the infrastructure would still have significant consequences for business customers and players.
"As for us, our system's architecture is quite compartmentalized. If one part of it gets breached, it won't affect everything and every client. But anyway, even a compromise of a small part of the infrastructure will be substantial. It will affect a lot of B2B customers and, of course, a lot of end users of our platform who are players. The security incident will probably transcend several borders and jurisdictions. In terms of consequences for private personal data, it's going to be substantial anyway."
He said AI has increased the probability of successful attacks by giving attackers far greater capacity to test multiple hypotheses. A task that once required days of manual effort can now be expanded dramatically with widely available models.
"My personal observation is that the likelihood of a successful attack has increased because attackers have much more capacity to test several hypotheses. Previously, testing several hypotheses on multiple targets took days of work for a penetration tester. Now, using mediocre models, attackers can industrialize this approach. It takes hours or days to test 10x, 100x, or 1,000x what was available to human attackers before. Even script kiddies armed with AI can successfully attack targets that were just not available to them before."
His assessment aligns with a wider industry concern that AI is lowering barriers to entry for less sophisticated attackers, even if the most advanced offensive work still requires deeper expertise and substantial computing resources.
Bychkov also argued that social engineering remains the most efficient route for attackers. In his view, AI has not changed the basic logic of cyber intrusion. It has lowered cost and increased speed.
"If I were a cybercriminal targeting an organization of any size, there's a famous quote (probably Bruce Schneier): 'Amateurs attack systems; professionals attack people.' In today's world, I would focus on attacking people because it is usually cheaper than firing up a frontier model to find a zero-day. If you successfully attack one high-profile employee, you get their credentials and access, allowing you to abuse the trust of other people and perform an attack from the inside. This maxim still holds in our AI era, but attacks have become cheaper and have a higher probability of success."
On the defensive side, he said Softswiss already uses AI tools in product security and monitoring, though not in a fully autonomous model.
"For the defensive side, the most obvious use of AI tooling is in product security. We employ AI tools for code security checks and supply chain analysis to reduce false positives and focus on real threats. We also use AI augmentation in security monitoring to uncover potential threat actor attacks efficiently. However, we are far from a humanless SOC. We don't fully trust decisions made by AI systems, so a human analyst still reviews final alerts and makes the decision on how to proceed."
That stance places Softswiss in the more cautious camp of adopters. Companies are adding AI to security workflows, but many still stop short of handing final response decisions to machines.
Bychkov closed with a question that is likely to become harder for the industry to avoid as AI spreads further into software supply chains and operations.
"We haven't solved formal software security verification yet, and now we face verifying AI models. How do we build trust around AI models in the future and verify they have no backdoors?"